'%3e%3cg id='Final-Copy-2_2_' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st0' d='M7.4,12.8h6.8l3.1-11.6H7.4C4.2,1.2,1.6,3.8,1.6,7S4.2,12.8,7.4,12.8z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg id='final---dec.11-2020'%3e%3cg id='_x30_208-our-toggle' transform='translate(-1275.000000, -200.000000)'%3e%3cg id='Final-Copy-2' transform='translate(1275.000000, 200.000000)'%3e%3cpath class='st1' d='M22.6,0H7.4c-3.9,0-7,3.1-7,7s3.1,7,7,7h15.2c3.9,0,7-3.1,7-7S26.4,0,22.6,0z M1.6,7c0-3.2,2.6-5.8,5.8-5.8 h9.9l-3.1,11.6H7.4C4.2,12.8,1.6,10.2,1.6,7z'/%3e%3cpath id='x' class='st2' d='M24.6,4c0.2,0.2,0.2,0.6,0,0.8l0,0L22.5,7l2.2,2.2c0.2,0.2,0.2,0.6,0,0.8c-0.2,0.2-0.6,0.2-0.8,0 l0,0l-2.2-2.2L19.5,10c-0.2,0.2-0.6,0.2-0.8,0c-0.2-0.2-0.2-0.6,0-0.8l0,0L20.8,7l-2.2-2.2c-0.2-0.2-0.2-0.6,0-0.8 c0.2-0.2,0.6-0.2,0.8,0l0,0l2.2,2.2L23.8,4C24,3.8,24.4,3.8,24.6,4z'/%3e%3cpath id='y' class='st3' d='M12.7,4.1c0.2,0.2,0.3,0.6,0.1,0.8l0,0L8.6,9.8C8.5,9.9,8.4,10,8.3,10c-0.2,0.1-0.5,0.1-0.7-0.1l0,0 L5.4,7.7c-0.2-0.2-0.2-0.6,0-0.8c0.2-0.2,0.6-0.2,0.8,0l0,0L8,8.6l3.8-4.5C12,3.9,12.4,3.9,12.7,4.1z'/%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/svg%3e)


Point of View | Page 1
OUR TAKE ON TRENDING STORIES
Hello. I’m Sue Denim, and I’ve spent the month looking at what organisations have been doing with personal data. Some used it to determine people’s livelihoods. Some considered using it to determine prices. Some fed it to artificial intelligence. Others stored it in buildings where the principal records-management system appeared to be “put it over there and hope the mould signs the retention policy”.
It has been a varied month.
The important lesson is that privacy has escaped the compliance department. It is now sitting in recruitment, pricing, marketing, artificial intelligence, workplace management, health systems and that account you created one evening because you wanted to watch somebody play a video game.
Here is what caught my eye, and what it could mean for organisations, employees, customers and ordinary people trying to get through the day without becoming a training dataset.
The price may now be looking back at you
The US Federal Trade Commission is consulting on a proposed enforcement policy concerning personalised pricing: the use of personal data to estimate what an individual might be willing to pay. Dynamic pricing is familiar. Flights become more expensive, hotel rooms fluctuate and the sandwich at the airport apparently arrives with its own mortgage application.Personalised pricing is more intimate. Rather than changing the price for everyone according to demand, a business may use information about a particular person, such as browsing behaviour or purchase history, to decide what price that person sees.
The FTC has not proposed banning every form of personalised pricing. Its concern is that businesses could mislead consumers if a price appears to be standard while personal data is quietly helping to determine it. [The FTC’s consultation explains the proposed approach](https://www.ftc.gov/news-events/news/press-releases/2026/08/ftc-seeks-comment-enforcement-policy-statement-regarding-personalized-pricing).
Sue’s translation: The website may not simply know that you want the shoes. It may be considering how desperately you want the shoes. For businesses, this is not only a pricing question. It involves marketing claims, customer expectations, profiling, transparency and the provenance of every signal entering the pricing model.Before introducing a personalised offer or price, an organisation should be able to explain:
- Which personal data influences the decision
- Where that information came from
- Whether the customer reasonably expects this use
- Whether different people can receive different prices
- What the customer is told
- Whether the result could unfairly exploit urgency or vulnerability
- How somebody can question or challenge the outcome
Calling the output an “individual value opportunity” will not make those questions disappear. It may, however, earn somebody a very exciting meeting with Legal.
For individuals, comparing prices while signed out or using a private browsing session may reveal differences, although it cannot establish why a price changed. Location, availability, promotions and timing may also influence the result.
The robot manager needs an escalation route
The Dutch Data Protection Authority fined Uber nearly €825 million over automated decisions that temporarily or permanently deactivated drivers’ accounts.According to the regulator, decisions concerning suspected fraud and low ratings were taken without human intervention. Losing access to the platform meant affected drivers could no longer accept rides or earn income. [The CNIL’s account of the cross-border decision explains the findings](https://www.cnil.fr/en/automated-decisions-uber-fined-nearly-eur-825-million).
This matters well beyond the gig economy.
Organisations increasingly use automated tools to shortlist applicants, score performance, detect fraud, prioritise investigations, allocate work and identify supposedly unusual behaviour. There is a natural corporate temptation to describe such tools as “decision support”. Sometimes that is accurate. Sometimes the human contribution consists of staring briefly at a score before clicking the button the system has already selected.
Sue’s question for the meeting: If the computer is wrong, who is both willing and authorised to say so? A meaningful human review needs more than a nominal approver. The reviewer should:- Understand the factors that influenced the decision
- Have access to relevant contextual information
- Be able to identify inaccurate or incomplete data
- Possess genuine authority to change the result
- Record why the decision was upheld or overturned
- Respond within a useful timeframe
An appeals mailbox monitored every second leap year does not constitute human oversight. Employees should also know when monitoring, scoring or automated decision-making affects them. If a system influences pay, shifts, access, promotion, discipline or continued employment, it deserves considerably more governance than the office coffee-ordering spreadsheet.
Your hobby would like to become an AI training exercise
In August, the Dutch privacy regulator warned Twitch users about a setting allowing their streams, images, chats and other information to be used for training Amazon’s generative AI.The regulator said the setting was enabled by default and advised users who did not want their material used in this way to switch it off. It highlighted that livestreams can include faces, voices, names, conversations and views inside people’s homes. [The Dutch authority’s notice provides details and opt-out instructions](https://autoriteitpersoonsgegevens.nl/actueel/ap-adviseert-twitch-gebruikers-zet-instellingen-uit-voor-delen-van-data-met-amazon-ai).
This is a consumer story with a very obvious workplace sequel. Employees are joining AI assistants, meeting tools, transcription services, design platforms and coding products with both personal and company accounts. The settings governing model training, product improvement and data retention can differ by service, subscription and account type.
A product being approved for corporate use does not necessarily mean every edition of it is approved. The enterprise version may have contractual controls that the free version does not.
Sue’s rule: “It was already on” is a description of a setting, not a privacy strategy. Businesses should check whether their approved AI services:- Use prompts, uploads or outputs for model training
- Enable training or product-improvement settings by default
- Treat free, individual and enterprise accounts differently
- Allow administrators to enforce settings centrally
- Retain deleted conversations or uploaded files
- Receive personal information about employees, clients or suppliers
- Provide an appropriate way to honour access, deletion and objection requests
Individuals should periodically inspect the privacy settings of creative, social and AI services. Pay particular attention after a notice announcing “exciting improvements”, a phrase that has occasionally meant exciting improvements for the company’s dataset.
The right to be forgotten also applies to people you did not hire
France’s data protection authority fined engineering and IT consultancy Extia €300,000 following complaints from former employees and job candidates about deletion requests.The regulator examined 265 requests made during 2024. More than three quarters had not been handled, or had not been handled satisfactorily. It also found failures to tell people what had happened after they exercised their rights. [The CNIL decision summarises the findings](https://www.cnil.fr/fr/sanction-non-respect-droits-personnes-extia).
Recruitment systems are enthusiastic collectors. A person uploads a CV for one vacancy and may quietly achieve immortality across an applicant-tracking platform, a shared drive, an interviewer’s inbox, a recruiter’s spreadsheet and a folder called `Potential People FINAL v4`.
Deleting the main applicant profile may therefore be only the opening act.
Sue’s recruitment test: Can you remove a candidate’s information from the places where recruitment actually happens, not merely the system shown during the audit? Organisations should map candidate information across:- Applicant-tracking systems
- Recruitment agencies and other processors
- Interview notes and assessment tools
- Email and collaboration platforms
- Talent pools
- Background-check providers
- Recorded interviews
- Artificial-intelligence screening services
- Locally maintained spreadsheets and exports
Automated deletion can help, but it does not remove the need to respond to the person. “The system probably dealt with it” is not a status update. For individuals, a deletion request should identify the account, vacancy or approximate application period. Keep a copy and note when it was sent. Depending on the applicable law and the organisation’s obligations, some information may need to be retained—but the organisation should explain what it is keeping and why.
The cloud was secure. The records were in a bathroom.
Ireland’s Data Protection Commission fined the Health Service Executive €645,000 after investigating the storage and retention of paper medical records.The investigation followed unauthorised access to records in disused former hospital buildings. During inspections, the regulator found documents affected by mould, water, animal droppings and general deterioration. Records were also found in disused bathrooms and cubicles, and in a shipping container inside a turf shed.
The DPC ordered a complete audit of storage facilities, better tracking of records, safe destruction where retention was no longer necessary, and removal of files from unsuitable locations. [The DPC decision describes the findings and corrective measures](https://dataprotection.ie/en/news-media/latest-news/data-protection-commission-announces-final-decision-following-inquiry-health-service-executive-hse).
This is the monthly reminder that personal data does not stop being personal because it has corners and smells faintly of filing cabinet. Many organisations have invested heavily in cloud security while retaining paper archives, backup media, retired laptops, old access cards and boxes inherited through mergers.
Sue’s storage policy: If nobody can explain what is in the room, who owns it or when it can be destroyed, locking the door is only delaying the plot. A proper information audit should include:- Off-site and third-party storage
- Closed offices and former premises
- Paper files awaiting scanning
- Archived employee and customer records
- Retired equipment and removable media
- Boxes acquired through mergers or restructuring
- Departmental cupboards that apparently pre-date electricity
Records must remain confidential, available and usable for as long as they are legitimately required. Retention is not achieved by keeping something indefinitely in conditions that make it inaccessible or unsafe.
At home, the same principle applies on a smaller scale. Old payslips, medical correspondence, photocopied identity documents and statements should not live forever in a drawer simply because the shredder is “a weekend job”.
We both know which weekend you mean. It does not exist.
A breach can affect people outside the customer list
France’s privacy regulator also fined Hôpital Privé de la Loire €500,000 following a health-data breach. The regulator identified weaknesses including insufficient external authentication, inadequate access controls and a lack of prompt detection for suspicious activity. It said credentials for one account allowed access to information concerning all hospital patients.The incident affected 524,867 patients and 202,246 people listed as trusted third parties. Although patients were informed, the trusted contacts were not notified directly. [The CNIL decision explains the security and notification failures](https://www.cnil.fr/en/sanction-fine-hopital-prive-loire).
That last point deserves attention. Organisations often design incident searches around their primary population: customers, employees, patients or account holders. Personal data about other people can be tucked inside those records:
- Emergency contacts
- Dependants and beneficiaries
- Guarantors
- Referees
- Witnesses
- Family members
- Authorised representatives
- Client contacts
- People mentioned in notes or correspondence
Sue’s incident-response question: Whose information was exposed—not merely whose account was involved? A notification assessment should follow the data, not the shape of the customer database. Secondary contacts may face different risks and may need different advice.This also matters when buying software. A supplier may promise that one compromised user cannot access unrelated records, but that claim should be tested through role design, access reviews, monitoring and realistic security exercises.
“Least privilege” should be an access-control principle, not the number of people invited to read the audit report.
Sue’s five-minute workplace privacy review
Before the next meeting acquires a steering group, try these questions:1. What personal data is entering our AI tools?Include prompts, meeting transcripts, uploaded documents, customer messages, source code, screenshots and generated outputs.
2. Which decisions about people are substantially automated?Look across recruitment, fraud, workforce management, customer eligibility, pricing and account suspension.
3. Can we actually complete a deletion request?Test the journey across the primary system, exports, suppliers and local copies. Do not accept “there is a button” as proof.
4. Where is the forgotten information?Include archives, warehouses, closed premises, cupboards, shared drives and historic platforms.
5. Does our incident process identify everyone in the data?Check dependants, emergency contacts, representatives and people mentioned within free-text records.
6. Are we changing prices, offers or treatment using personal profiles?If so, document the inputs, explain the practice properly and test the outcomes.
Sue’s five-minute personal privacy review
For people whose job description does not contain the word “governance”:- Review training and product-improvement settings in AI and creative services
- Use unique passwords and multifactor authentication
- Close accounts you no longer use
- Check which applications can access your email, files and social accounts
- Keep copies of important privacy or deletion requests
- Compare significant prices without assuming every difference is personalised
- Securely destroy documents you no longer need
- Avoid putting confidential work information into personal AI accounts
You do not need to spend Sunday reading every privacy notice ever written. Nobody should lose a Sunday like that—not even the person who wrote them.
Start with services holding information that could affect your health, money, employment, identity or reputation.
Sue’s final word
These developments come from different countries, sectors and legal proceedings. They do not prove that every business is personalising prices, every automated system is unlawful or every archive is being slowly consumed by wildlife.They do reveal a consistent practical problem: organisations frequently lose sight of personal data once it moves outside the process for which governance was originally designed.
A candidate becomes a record in several recruitment tools. A driver becomes a score. A trusted contact becomes a field inside somebody else’s medical file. A livestream becomes training material. A customer becomes a predicted willingness to pay. A paper record becomes part of the building.
Good privacy management keeps the person visible throughout that journey.
Until next month, please remember: if your data strategy requires the sentence “technically, they agreed”, Sue has follow-up questions.
April, darling, was less “spring awakening” and more “security faceplant in slow motion.” Let’s unpack the chaos.
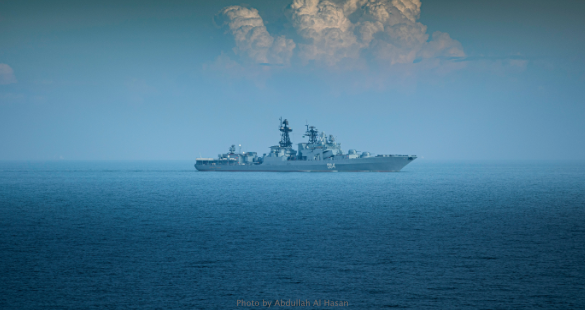
The €5 Gadget That Humiliated a €500 Million Warship. Now this, this, is art.
The Dutch Navy, armed with a €500 million warship (HNLMS Evertsen, no less), gets outplayed by what is essentially the technological equivalent of loose change down the back of a sofa.A €5 Bluetooth tracker. From Amazon. No cloak, no dagger, just vibes and free shipping.
Journalists, clearly bored of watching defence PR videos, spotted a tiny operational detail: packages get X-rayed… letters don’t. And since anyone can send post to the navy (because why not?), they popped a tracker into a letter addressed to the gloriously generic “Jan Jansen.”
Fast forward: that letter takes a scenic European tour, hops a flight to Crete, boards the warship, and voilà—instant DIY naval surveillance.
The captain even flipped off the AIS tracker, presumably thinking he’d gone full stealth mode. Adorable. Meanwhile, the journalists are sat there watching his route like it’s Deliveroo.
Tracked all the way to Cyprus. Game over.
Moral of the story? You can spend half a billion on defence tech, but if your mailroom’s running on vibes, you’re basically broadcasting your location with a handwritten invite.
Ubuntu’s AI Era. Because Apparently We Haven’t Suffered Enough.
Canonical has decided that what the world really needs right now… is more AI. Specifically, AI baked directly into Ubuntu.Because nothing says “stable, reliable operating system” like sprinkling in a bit of experimental automation and hoping for the best.
They’ve split it neatly into:
- Implicit AI, sneaky enhancements quietly tinkering under the hood.
- Explicit AI, the loud stuff: agents, automation, content generation… the whole circus.
And yes, they’ve promised it won’t turn Ubuntu into “an AI product.” Sure. And my gym membership is definitely going to pay off this year.
Look, maybe it’ll be brilliant. Maybe it’ll streamline workflows and make sysadmins weep tears of joy. But history suggests we’re about three updates away from an OS that insists on “helping” you rewrite bash scripts in poetic form.
My verdict? I'm packing my bags and leaving Ubuntu like it just started talking about NFTs again.
Signal Messages That Refused to Die.
Ah yes, the app famous for making messages disappear… except when they don’t.In a twist that’s less “Mission Impossible” and more “forensic bingo,” the FBI managed to recover deleted Signal messages, even after the app itself had been removed.
Turns out, Apple had a bit of a housekeeping issue:
- Notifications that should’ve been wiped… lingered.
- Logs that should’ve been scrubbed… weren’t quite scrubbed enough.
Apple’s patched it now, tightening up redaction and fixing the leak. Signal gave them a polite nod.
Unfortunately for the criminals involved, the patch arrived slightly too late to save their weekend plans. They’re now enjoying government accommodation.
Takeaway? “Deleted” doesn’t always mean gone. Sometimes it just means “waiting to ruin your day in court.”
Final Word.
April wasn’t subtle. It was a loud, slightly embarrassing reminder that:- The weakest link is rarely the expensive tech—it’s the overlooked process.
- AI is creeping into everything, whether you like it or not.
- And “secure” apps still depend on the ecosystem around them behaving properly.
In other words: the basics still matter. Always have.
Now if you’ll excuse me, I'm off to post a Bluetooth tracker to someone important. Purely for research, of course.
Sources
- Omroep Gelderland (Dutch Navy tracking investigation).- Dutch Ministry of Defence (public footage).
- Canonical (Ubuntu AI announcements).
- Apple Security Updates.
- Signal statement on vulnerability fix.
Hackers, Hit Lists & Comebacks: The Internet’s Favourite Crime Forum Refuses to Die.
Just when you thought the cyber underworld might take a breather, it instead reached for the espresso and doubled down.
ShinyHunters Declares Open Season
In last week’s episode of “Threat Actors Behaving Badly”, ShinyHunters made it abundantly clear: BreachForums clones were on borrowed time. No vague threats. No cryptic riddles. Just a clean, direct warning: “We will begin taking targeted action… You know who you are.”
Nothing says “good morning” like a personalised cyber death sentence. And, as promised, the follow-through arrived promptly. One clone admin was unmasked (never a great career milestone), and more importantly, the BreachForums Version 5 user database was leaked into the wild.
Now it’s being hoovered up by everyone with a vested interest, law enforcement, rival threat actors, and security researchers. Think of it as the internet’s least exclusive VIP list.
Fear Factor: 10/10. The reaction? Immediate.
Several well-known figures behind BreachForums clones quietly packed up shop and disappeared faster than unsecured S3 buckets after a headline breach. For a brief moment, it looked like ShinyHunters had achieved something governments have been trying to do for years, scare cybercriminals into early retirement.
Imagine being more feared than global law enforcement. That’s not influence… that’s branding.
Plot Twist: The Forum Strikes Back
But before anyone could celebrate too loudly, the inevitable happened. BreachForums is back. Again. Because of course it is.
The “new” iteration wasted no time setting the tone “Not an exit scam… treat this as the real BreachForums… use new identities and improve OPSEC.”
A clean slate, apparently. Nothing says “fresh start” like politely reminding users not to reuse the same identity that just got leaked. It’s less phoenix-from-the-ashes, more hydra-with-a-hosting-plan.
Meanwhile, In the Real World…
While cybercriminals were busy rebranding, the Director of the FBI, Kash Patel, had a rather inconvenient week, his personal email was compromised. Allegedly by Iranian-backed actors. Not ideal.
The response? Swift, decisive, and very American: Within five hours, the U.S. government dropped a $10 million bounty for information on anyone conducting state-sponsored cyber attacks.
That’s not just escalation. That’s turning cyber attribution into a high-stakes game show. “Hack the US, win a prize, or have one put on your head.”
And Now… Surveillance, But Make It Stylish
As if things weren’t already lively, NVIDIA decided to enter the chat with a new always-on, low-power facial recognition chip. Designed for consumer devices. Laptops, drones, robotics. You know, the usual. Naturally, this has triggered mild concern, and by “mild,” we mean the entire team collectively reaching for metaphorical tinfoil hats.
CEO Jensen Huang has already been vocal about supporting defence initiatives, and with NVIDIA partnering up with Palantir (yes, that Palantir), the vibes are… let’s say strategically ominous.
We’re not saying it’s Skynet. We’re just saying Skynet would probably start like this.
This month wasn’t just chaotic, it was revealing.
• Cybercriminal ecosystems remain fragile, but far from defeated
• Reputation now carries more weight than infrastructure
• Nation-state tensions are bleeding further into public cyber discourse
• And big tech continues to blur the line between convenience and surveillance
In short: the internet remains undefeated in its ability to escalate everything, everywhere, all at once. Stay tuned. It’s only getting louder.
Sources
• Statements attributed to ShinyHunters
• BreachForums activity and database leak reporting
• U.S. Rewards for Justice announcement (X)
• Public reporting on FBI Director email compromise
• NVIDIA product announcements and partnerships with Palantir
Garlic Gone Wild: How 700,000 Bots Tried to Hijack the Anonymous Internet
If there was an award for “Most Chaotic Entrance of the Month,” Kimwolf would already be clearing shelf space.
The headline act? A botnet, allegedly powered by around 1.4 million compromised IoT devices, because apparently your smart toaster yearns for cybercrime, decided it would take a little stroll into the I2P network. And by “a little stroll,” we mean it tried to shove roughly 700,000 hostile nodes through the door at once.
Subtlety was not invited.
First, A Quick Refresher
I2P, for the uninitiated, is anonymity infrastructure with a slightly different flavour to Tor.Tor is your classic onion routing setup, layered encryption, peel it back one relay at a time.
I2P? It prefers garlic routing. Multiple encrypted messages bundled together into one transmission. Efficient. Discreet. Mediterranean, almost.
It also separates inbound and outbound tunnels, making traffic analysis considerably trickier. Clever architecture. Early-2000s vintage. Niche, but purposeful. Typically running at around 15,000 active nodes, not sprawling, but sturdy.
Until 3rd February.
When 15,000 Meets 700,000
Kimwolf’s operators were already feeling the heat. Security researchers had reportedly taken aim at around 500 of their core command-and-control servers, and that tends to ruin anyone’s week.So the alleged strategy? Strengthen and obfuscate the botnet by leveraging I2P’s anonymity. Blend in. Disappear into the encrypted garlic mist.
Instead, they stampede-charged the network with 700,000 malicious nodes.
The result? Less “stealth infiltration.” More “elephant in a porcelain factory.”
The sudden flood completely swamped I2P’s routing capacity. Legitimate routers froze. Connections buckled. The protocol choked under the weight. In trying to hide inside the network, they effectively body-slammed it.
Cyber subtlety, this was not.
A Self-Inflicted Sybil
Shortly after, the operators reportedly admitted on Discord that they had accidentally triggered a Sybil attack, the technical term for flooding a decentralised network with fake nodes until the real ones can’t function properly.In short: they tried to make themselves harder to track and instead DoS’d the very anonymity layer they were hoping to weaponise.
It’s the digital equivalent of hiding in a crowd by driving a tank into it.
For added context, this is the same botnet ecosystem believed to have powered one of last year’s largest DDoS attacks, peaking at 31.4 terabits per second. This is not small-time mischief. This is industrial-grade disruption.
And yet, even industrial-scale botnets can trip over their own ambition.
The Counterpunch
To I2P’s credit, the development team moved quickly. Within days, updates were released featuring:* Post-quantum encryption enhancements
* Sybil attack mitigations
* Stability improvements for saturated routing environments
The network remains operational, though not yet fully restored to its pre-incident scale and stability. Recovery in decentralised ecosystems is more marathon than sprint.
But there’s a quiet irony here.
An anonymity network designed to resist surveillance was stress-tested not by regulators or law enforcement, but by criminals overplaying their hand.
The Bigger Picture
This wasn’t just a botnet mishap. It was a live-fire demonstration of how fragile decentralised systems can become when weaponised at scale.It also highlights a recurring truth in cyber operations: scale amplifies power, but it also amplifies mistakes.
Kimwolf tried to disappear into the shadows. Instead, it turned on the floodlights.
Sometimes the garlic bites back.
January wasted no time reminding everyone that the internet never forgets, and karma has a calendar.
We’ll start with Empire Market, one of the largest dark web marketplaces of its era. Operating between 2018 and 2020, Empire processed over four million transactions and became a fan favorite in underground circles. It offered the usual greatest hits: cannabis, cocaine, stolen credit cards, counterfeit goods, and malware, all wrapped in a slick interface that made avoiding street deals feel almost… convenient.
Then, in 2020, Empire did what so many before it had done: exit scammed its users for an estimated $30 million in crypto and vanished into the night. Or so they thought.
Fast-forward to today, and reality has finally caught up. Raheim Hamilton, the market’s co-creator, has entered a plea deal and is set to be sentenced on June 17 in the Northern District of Illinois. There’s a mandatory minimum of ten years in federal prison, proving once again that while crypto transactions are fast, consequences can take their sweet time.
Next up: BreachForums, or more accurately, the ongoing BreachForums reboot disaster.
At this point, there have been so many failed resurrection attempts that calling it “a comeback” feels generous. Currently, there are two competing versions of BreachForums operating simultaneously on the dark web. In true crime-forum fashion, they absolutely hate each other. Let’s call them BF1 and BF2.
BF1’s admins managed to leak BF2’s private Telegram staff chats, posting them to Doxbin alongside a full dox of BF2’s admin, including name, religion, education, and approximate location. Because why stop at screenshots when you can go full scorched earth? Not to be outdone, BF2’s admin allegedly obtained the personal phone numbers of BF1’s admins and possibly staff, and reportedly started calling one of their mothers. Yes. Someone’s mum.
Law enforcement, meanwhile, is likely watching this unfold like it’s a Netflix limited series. This kind of infighting doesn’t just destroy forums, it creates beautifully detailed evidence trails that future arrest warrants are built on.
And finally, January ended with a reminder that crypto crime consequences vary wildly depending on jurisdiction.
The Chinese government executed 11 members of the Ming crime family for operating a massive crypto scam empire out of Myanmar. The operation employed more than 10,000 people, running large-scale “pig butchering” scams, long-term romance frauds designed to drain victims emotionally and financially.
Employees who tried to leave were reportedly beaten or killed. The operation collapsed in 2023 when members of the crime family were captured in Myanmar and handed over to China by ethnic militias. The verdict? Swift. Final. Unambiguous.
So, January in summary:
- Exit scammers finally got exit scammed by reality
- Dark web forums turned into soap operas
- And one government made it very clear where it stands on crypto fraud
New year. Same internet.
This months cyber spotlight, vulnerability chat & privacy headlines.
Breach, Bots & Deepfake Dramahttps://breachaware.com/research/breach-bots-and-deepfake-drama
A total of 9 breach events were found and analysed resulting in 1,860,834 exposed accounts containing a total of 21 different data types of personal datum. The breaches found publicly and freely available included 1M+ Valid USA Forex 1 Million, Aternos [2], Costco - Taiwan, Do Big GPT and Alain Afflelou.
Encrypted Mayhem, Mega Leaks & AI Under Fire.
https://breachaware.com/research/encrypted-mayhem-mega-leaks-and-ai-under-fire
A total of 24 breach events were found and analysed resulting in 14,347,979 exposed accounts containing a total of 32 different data types of personal datum. The breaches found publicly and freely available included Instagram, Thermomix, Air Miles España Loyalty Program - Travel Club, Giglio and Qantas [Sample Data].
One Breach to Rule Them All: Why No Organisation Is Ever “Unaffected”
https://breachaware.com/research/one-breach-to-rule-them-all-why-no-organisation-is-ever-unaffected
A total of 19 breach events were found and analysed resulting in 52,354,695 exposed accounts containing a total of 36 different data types of personal datum. The breaches found publicly and freely available included ULP Alien Txt File - Episode 31, ULP 0038, ULP 0039, Stealer Log 0550 and WebDo.
If you thought the month was going to be quiet, you clearly underestimated the internet’s ability to resurrect decade old controversies and annoy law enforcement in entirely new ways.
Let’s start with a true crypto classic: Silk Road.
Yes, that Silk Road, the Tor based marketplace launched in 2011 by Ross Ulbricht, shut down by the FBI in 2013, and followed by a legal saga so extreme it still makes civil libertarians wince. Ross was handed two life sentences without parole at the age of 26, aided by a deeply questionable murder for hire narrative that continues to raise eyebrows to this day.
Fast forward through a decade long “Free Ross” campaign, a Trump pardon last year, and suddenly we’re asking the question law enforcement hoped would never resurface: Did they actually find all the Bitcoin?
According to Coinbase director Conor Grogan, roughly 430 BTC, currently worth about £27 million, remains linked to dormant Silk Road wallets that Ross may still control. These wallets had been sitting quietly, minding their own business, until December 10th, when 176 transactions fired off in under four hours. Casual.
Ross, speaking from prison, has previously promised he’d never break the law again if released. Which is great. Unfortunately for the authorities, Bitcoin moving ≠ laws being broken, just nerves being shattered. One imagines the feds aren’t thrilled watching digital money they’d very much like to confiscate suddenly start stretching its legs. If that Bitcoin gets laundered properly, it’ll be about as traceable as their original crypto expertise circa 2013.
Speaking of law enforcement frustration, let’s talk GrapheneOS.
This privacy focused operating system, running exclusively on Google Pixel phones, is estimated to be used by 250,000 to 400,000 people worldwide. The number is fuzzy because, and brace yourself, it doesn’t collect telemetry or usage data. Imagine building tech that doesn’t spy on its users. Radical.
Sure, that’s tiny compared to the billions glued to Android and iOS, but GrapheneOS has carved out a loyal following among privacy advocates and cybersecurity professionals. Unfortunately, it’s also carved out a migraine for law enforcement.
Their favourite digital forensics toy, Cellebrite, can’t crack these devices. Tragic. As a result, agencies across Europe and the US have begun profiling Pixel users, suggesting that criminals must obviously be choosing secure phones on purpose. Because heaven forbid regular people want privacy too.
Earlier this month, things escalated. GrapheneOS announced it was shutting down all operations in France, citing outrageously false and unsubstantiated claims made by French law enforcement, claims that were then happily laundered through state and corporate media as fact. The project says it was never given the opportunity to respond.
So, to recap:
- Old Bitcoin is waking up
- Privacy tech is doing its job
- Law enforcement is… not coping well
Honestly, if this is the future, it’s going to be a very entertaining one.
Smarter Protection Starts with Awareness
Data Breach Scan, Check Any Domain for Free https://breachaware.com/scanThis months cyber spotlight, vulnerability chat & privacy headlines.
Dark Web Admin Exposed, Trident Ransomware Strikes & Airbus Issues Critical Patch.https://breachaware.com/research/dark-web-admin-exposed-trident-ransomware-strikes-and-airbus-issues-critical-patch
A total of 34 breach events were found and analysed resulting in 6,558,157 exposed accounts containing a total of 39 different data types of personal datum. The breaches found publicly and freely available included ULP 0037, Stealer Log 0549, Stealer Log 0548, Ekonika and 123 Casting.
Dark Web Busts, CLOP Hits Ivy League & Global Exploits Erupt.
https://breachaware.com/research/dark-web-busts-cl0p-hits-ivy-league-and-global-exploits-erupt
A total of 7 breach events were found and analysed resulting in 342,933 exposed accounts containing a total of 19 different data types of personal datum. The breaches found publicly and freely available included Queen Mary University of London, France Casse, Artists and Clients, Refer Life and e-Retail.
Ransomware Slumps, RaidForums Relaunches & VAS Crackdown Success.
https://breachaware.com/research/ransomware-slumps-raidforums-relaunches-and-vas-crackdown-success
A total of 17 breach events were found and analysed resulting in 2,686,286 exposed accounts containing a total of 30 different data types of personal datum. The breaches found publicly and freely available included France Travail, Miljodata, Corporate Mails Dump, 1 Million Pholoniex Email List [Sample] and Emirates Philatelic Association - EPA.
Forums Get Doxed, RaidForums Speedruns Death & Microsoft Blinks.
https://breachaware.com/research/forums-get-doxed-raidforums-speedruns-death-and-microsoft-blinks
A total of 12 breach events were found and analysed resulting in 6,036,789 exposed accounts containing a total of 54 different data types of personal datum. The breaches found publicly and freely available included ULP Alien Txt File - Episode 29, Venezuela Citizen Databases, Turing, Webové Stránky and WithPropel.
ATOs Explode, Insider Betrays CrowdStrike & FBI Looms Over Carding Empire.
Account Takeover scams are booming, which is great news for nobody except threat actors and whatever dodgy Telegram groups they hang out in.
The FBI announced last week that ATOs have skyrocketed this year, with criminals pocketing a casual $262 million since January. Victims have filed 5,100+ complaints, which is honestly impressive given that most people don’t even bother reporting crime unless it interrupts your favourite video streaming app.
Threat actors are now going full chef’s kiss with their phishing emails, sliding into online banking and payroll systems like they’re speed-running a tutorial. They’re also abusing SEO, which is deeply offensive, Google rankings used to be for small businesses, influencers, and pyramid schemes… not cybercriminals trying to steal your 2FA codes.
The FBI is once again shouting into the void about using MFA and stronger passwords. Which, let’s be honest, means half of the world will continue using Password123 until the heat death of the universe.
In the category of “world’s worst criminals,” we have the insider at CrowdStrike who sold out access to one of the biggest cybersecurity companies in the world… for $25,000.
Yes.
Twenty. Five. Thousand. Dollars.
Before tax.
The threat actor collective Scattered Lapsus$ Hunters, or ShinyHunters, or whatever their rotating name of the week is, claims they paid the insider for screenshots of internal systems. They even got SSO authentication cookies… but by that point, the insider had already been caught, booted, and presumably escorted out of the building with the world’s most awkward cardboard box.
CrowdStrike fired him immediately (obviously), notified the relevant agencies, and is now probably installing retina scanners in the bathrooms. Moral of the story: If you’re going to betray a Fortune 500 cybersecurity company, maybe charge more than the price of a used Honda.
A cyber intelligence watchdog has noticed something very interesting happening on a well-known carding site, the kind that sells stolen credit cards, bank credentials, and probably your grandmother’s debit PIN.
The DNS records appear to have been touched by… the FBI. Which means one of two things:
1. A major FBI takedown is incoming,
2. Or the carding site admins have finally messed up so badly that even their DNS got stage-fright.
If the feds have seized control, this would be a devastating blow for the carding underground, and a massive win for law enforcement. It’s basically the cybercrime equivalent of waking up to find out your favourite illegal marketplace now redirects to a big, angry FBI splash page.
We’ll keep an eye on this one. It’s either a takedown, a sting, or a spectacularly funny misconfiguration.
Smarter Protection Starts with Awareness
Data Breach Scan, Check Any Domain for Free https://breachaware.com/scanThis months cyber spotlight, vulnerability chat & privacy headlines.
Malware Makers Arrested, Fake CAPTCHAs Get Thirsty, and Teen Ransomware Falls Apart Instantly.https://breachaware.com/research/malware-makers-arrested-fake-captchas-get-thirsty-and-teen-ransomware-falls-apart-instantly
A total of 21 breach events were found and analysed resulting in 12,901,859 exposed accounts containing a total of 28 different data types of personal datum. The breaches found publicly and freely available included ULP 0035, MyVidster, TurkNet, César Vallejo University and Wbia.
DeFi Drained, Rogue AI Unleashed, and Ransomware “Good Guys” Turned Villains.
https://breachaware.com/research/defi-drained-rogue-ai-unleashed-and-ransomware-good-guys-turned-villains
A total of 35 breach events were found and analysed resulting in 20,016,481 exposed accounts containing a total of 31 different data types of personal datum. The breaches found publicly and freely available included ULP Alien TxT File - Episode 27, MYM, 100 Million ULP, ULP 0036 and Stealer Log 0546.
Crypto Scammer Dismembered, FBI Director Doxxed & Cybercrime Forums Crushed.
https://breachaware.com/research/crypto-scammer-dismembered-fbi-director-doxxed-and-cybercrime-forums-crushed
A total of 18 breach events were found and analysed resulting in 4,940,527 exposed accounts containing a total of 30 different data types of personal datum. The breaches found publicly and freely available included ULP Alien Txt File - Episode 28, Stealer Log 0547, joom-dmps, Crypto Email Database 2025 and TISZA Világ.
Shiny Hunters Level Up, Crypto Thugs Jailed & Cloudflare Shakes the Internet.
https://breachaware.com/research/shiny-hunters-level-up-crypto-thugs-jailed-and-cloudflare-shakes-the-internet
A total of 10 breach events were found and analysed resulting in 380,308 exposed accounts containing a total of 23 different data types of personal datum. The breaches found publicly and freely available included Millicom.com, L’ Assurance Retraite, Conasems (Conselho Nacional de Secretarias Municipais de Saúde), Secretariat of Public Education (SEP) - Mexico and Nemopro.
WHAT THE PR!V*CY
THE LATEST CURATED INTEL FROM OUR RESEARCH CENTRE
Listen to our podcast, where Andrew, the visionary CEO of BreachAware, sits down with unsung heroes of the cyber security industry. Get ready to uncover the stories and insights of industry trailblazers you might not have heard of before, as they share their experiences, opinions, and insider intel. But beware, it's not all serious talk—expect a healthy dose of humour (and the odd cussing) sprinkled throughout the conversation.


Weekly Summary
SPOTLIGHT, VULNERABILITY CHAT & PRIVACY HEADLINES
SCHEDULE A DEMO
MAKE THE SMART CHOICE TODAY
